Discover
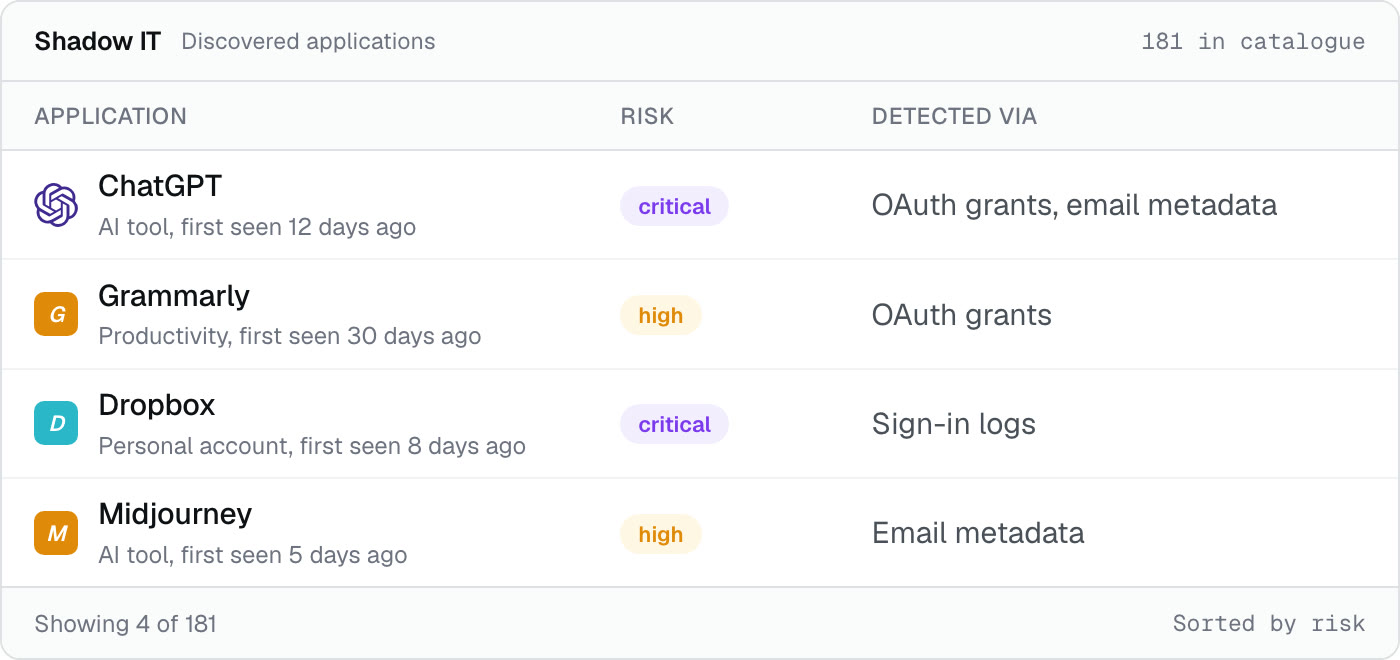
AI tools nobody approved
Find the AI tools reading your mail, without deploying anything.

What the industry reports
- 81%of employees use AI tools their employer has not approvedUpGuard, State of Shadow AI 2025
- 93%of executives and senior managers use them tooUpGuard, State of Shadow AI 2025
- 3 in 4shadow AI users have put possibly sensitive information into oneUpGuard, State of Shadow AI 2025
The moment
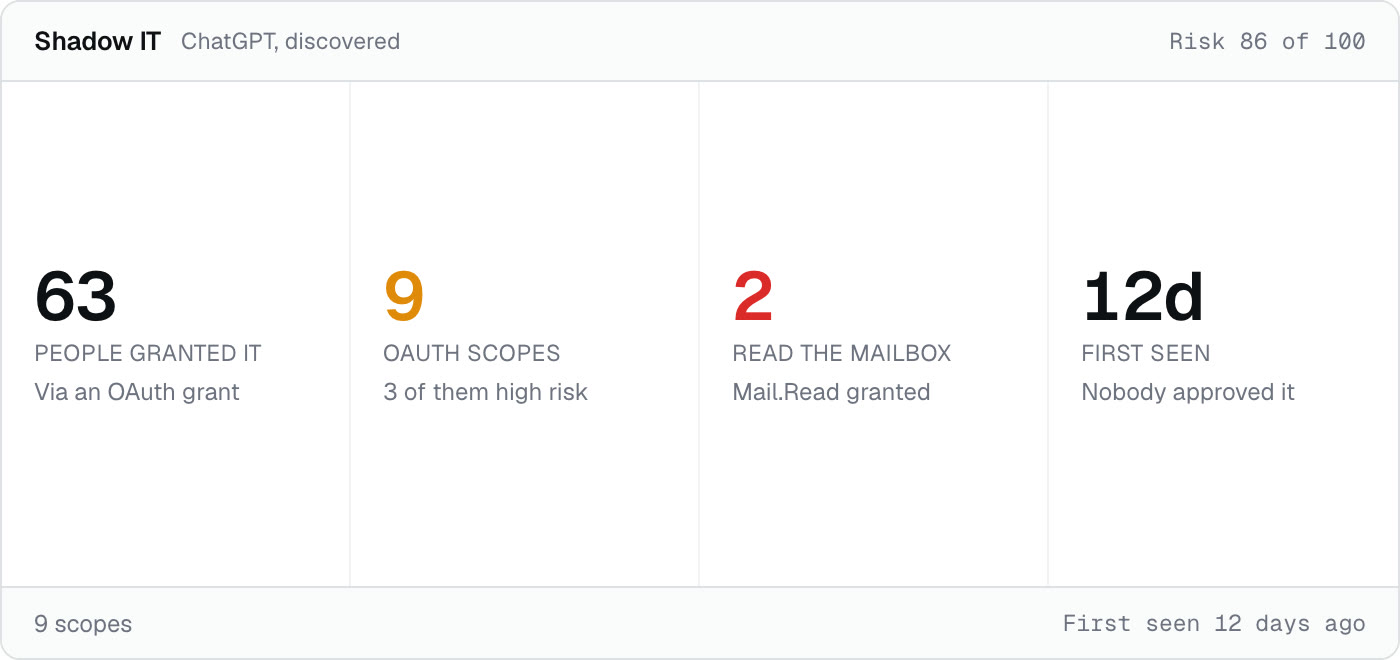
Someone signed into an AI notetaker with their work account on Tuesday. It asked for Mail.Read. They clicked allow.
For whoever gets asked what people are using.
Discovery starts with no deployment
Sign-in logs, OAuth grants and email metadata you already hold.
A grant is judged on what it reaches
Mail.Read on a notetaker is not the same risk as a profile read. The scope analyzer says what the permission opens.
Sanction, review or block, as one decision
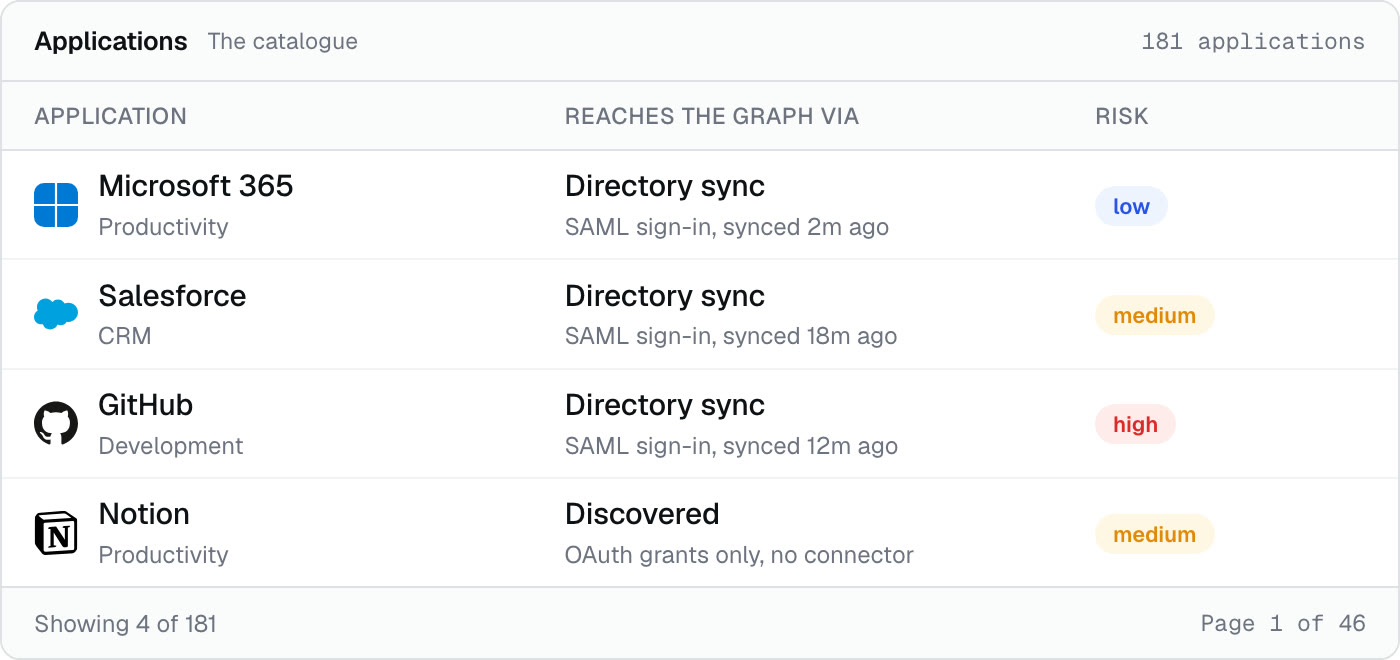
Every discovered tool carries an owner, a status and a score. Nobody has to run a survey to learn what people are using.
What you get
Everything this covers.
Discovery
- Sign-in logs, OAuth grants and email metadata you already hold
- A browser extension for what the directory never sees
- Nothing to install on a laptop and no proxy to stand up
Risk assessment
- Every application scored from 0 to 100, with its OAuth scopes weighed in
- Scopes read out with who consented, when and from where
- AI tools flagged as they arrive in the catalog
Governance
- Sanction, review or block, as one decision on the application
- Every OAuth grant to an app revoked in one action
Ongoing control
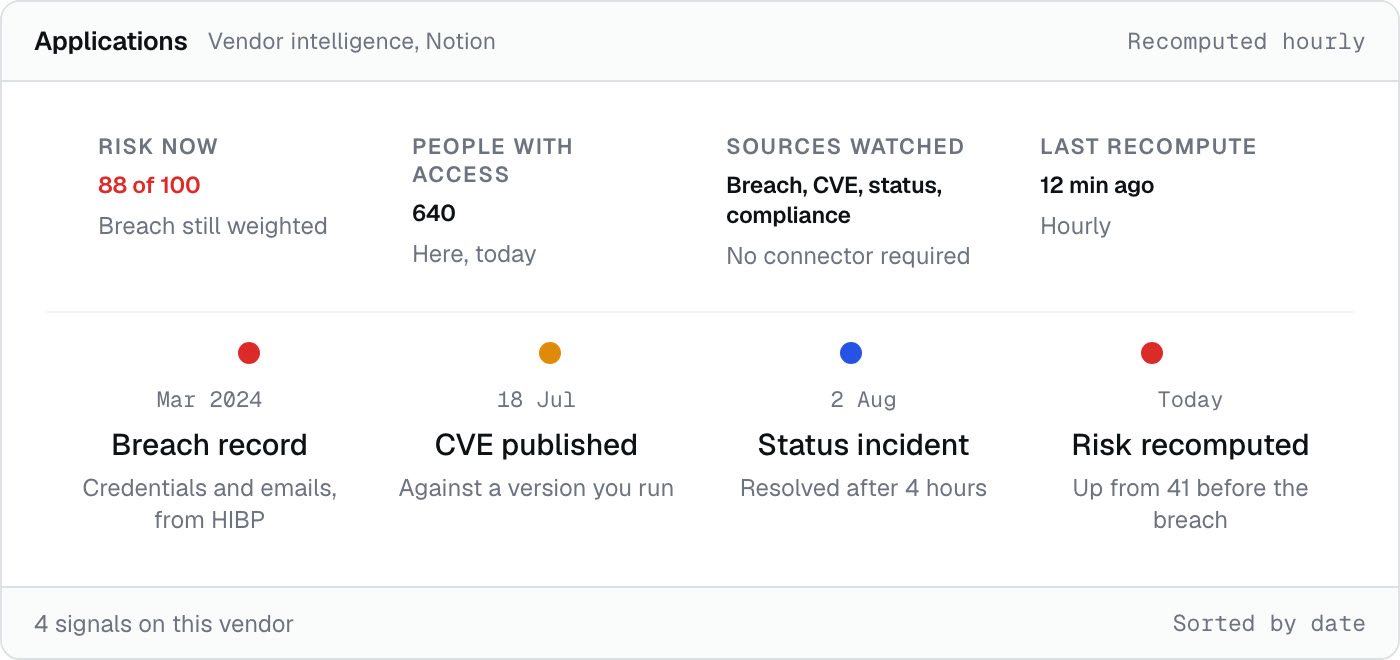
- Vendor breach records, CVEs and status incidents sit on each app, beside the people who use it