What the industry reports
- 45%of former employees admit signing back in to view, take or delete dataPonemon Institute, 2025
- 32%of organizations take more than seven days to fully deprovision a leaverOneLogin, IT decision-maker survey
The moment
Their last day was Friday. On Monday the sessions are still live, the groups still list them, and the OAuth grants never expired.
For IT operations, on both ends of the org chart.
The directory change is the trigger
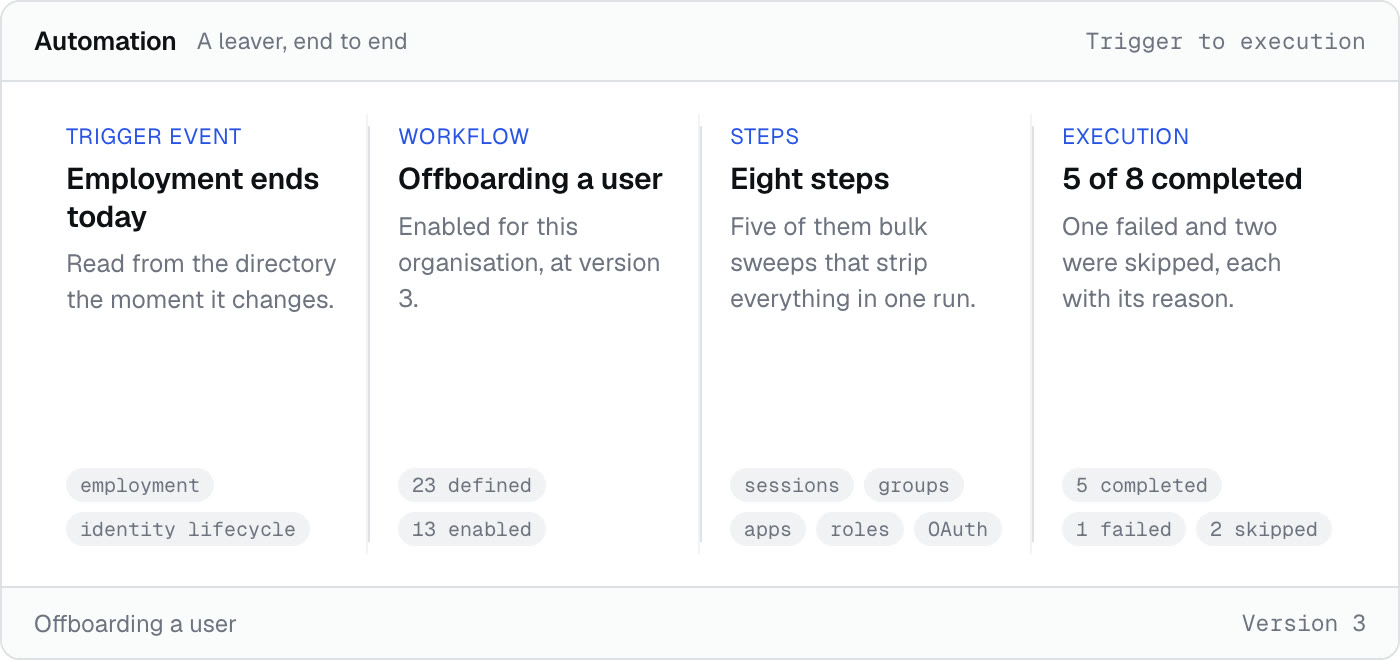
The run starts when employment ends in the directory, with no ticket in between.
One run strips everything
Sessions, groups, application assignments, directory roles and OAuth grants. Five kinds of access that usually need five people.
An unsupported step says so
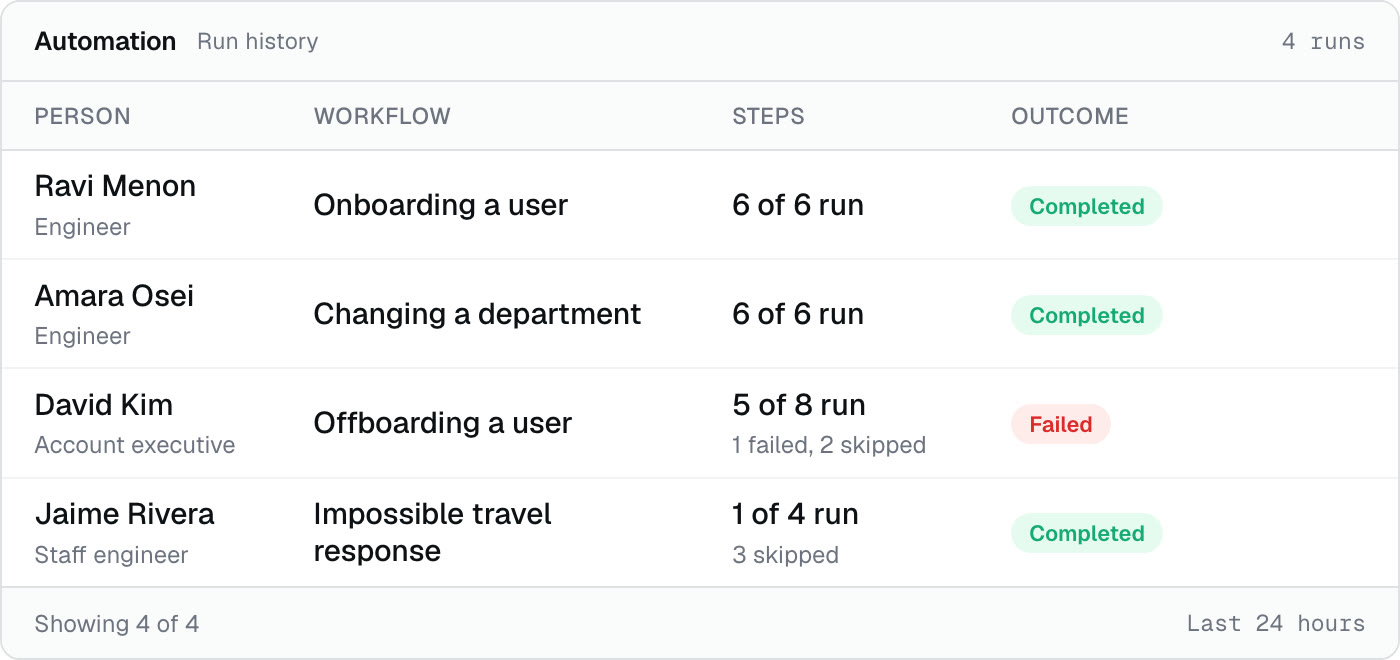
Where a connector cannot do something, the step is skipped with its reason on the record.
What you get
Everything this covers.
Joiner
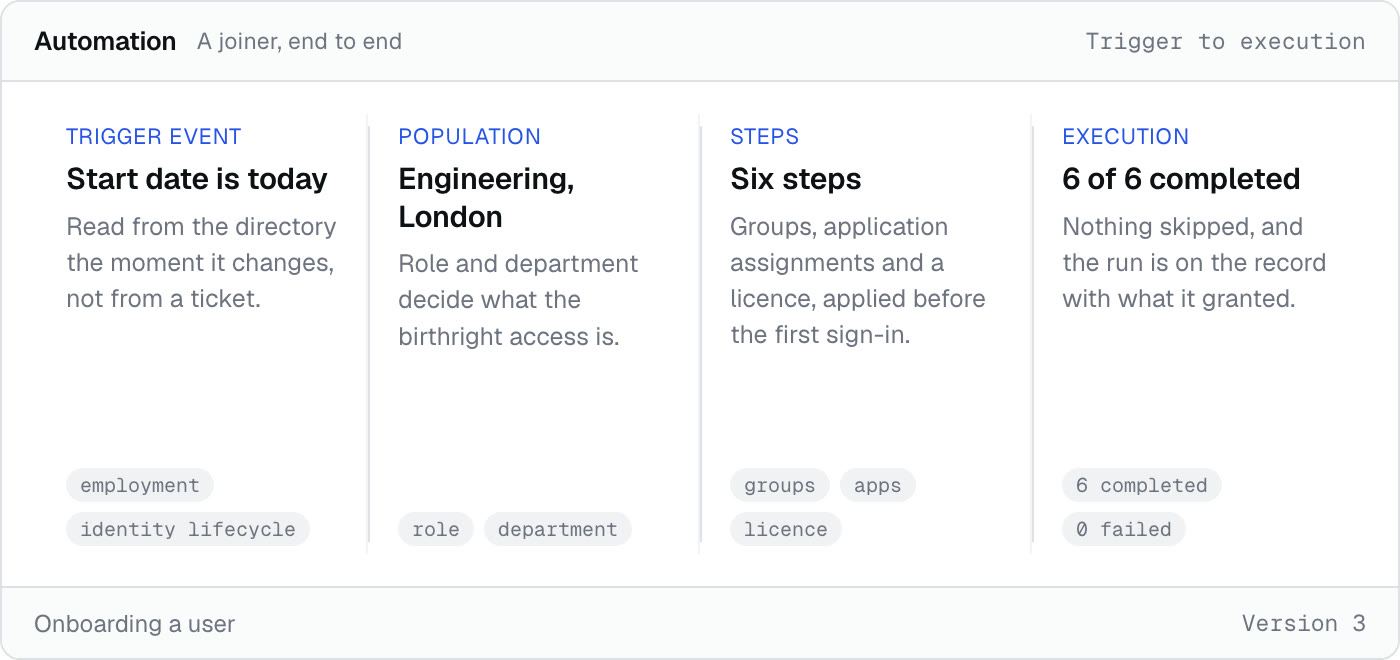
- Birthright access by role and department when the account is created
- The directory change is the trigger
Mover
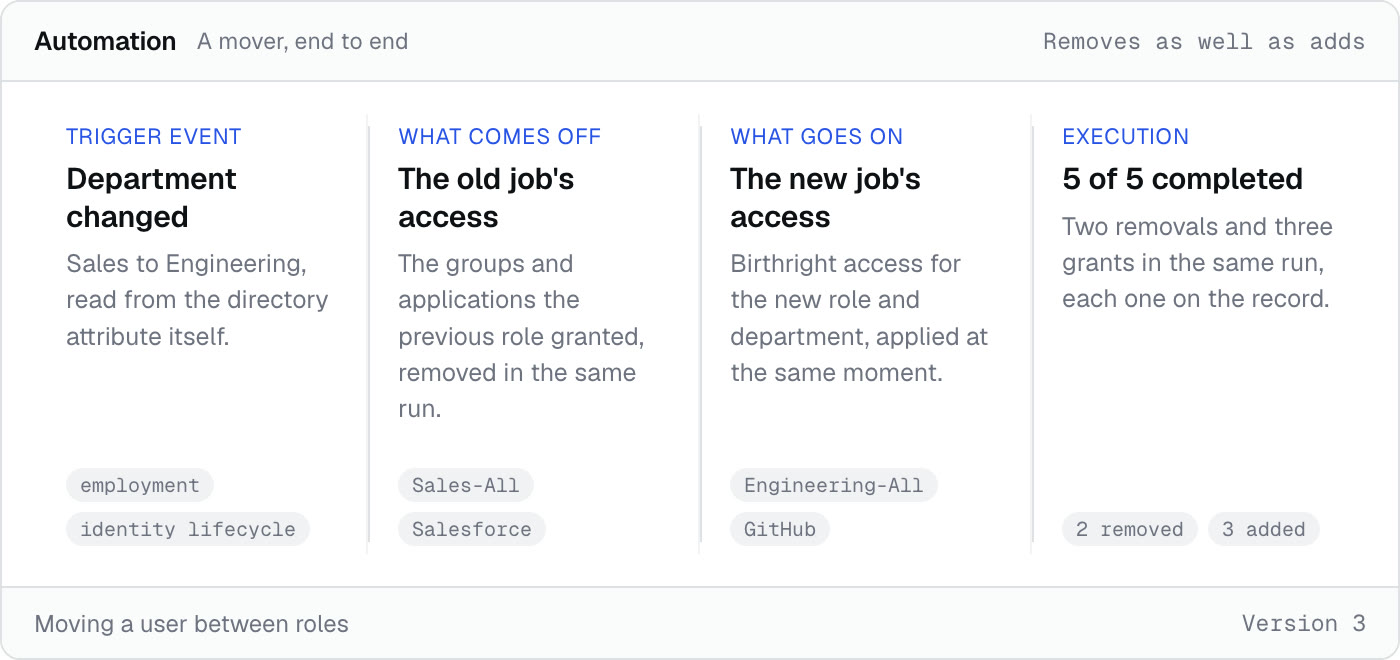
- Out of the groups and applications the old job needed
- Into the ones the new job does, in the same run
Leaver
- Sessions, groups, app assignments, roles and OAuth grants in a single run
- A step a connector cannot do is skipped with its reason
Evidence
- Workflows versioned, with a snapshot of the version that ran
- A record per step: what ran, what changed, what failed
- Notified in the product, by email, on Slack or by webhook