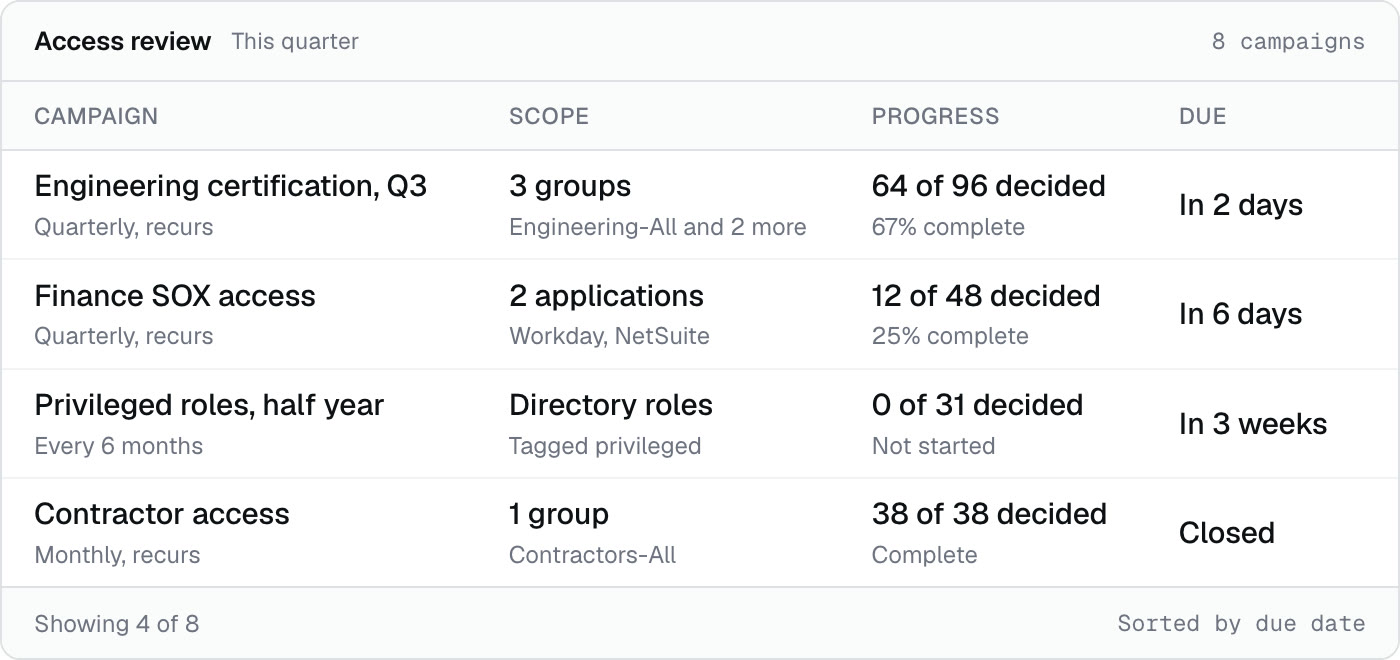
Govern and Detect
No standing access
Admin that arrives for four hours and leaves on its own.

What the industry reports
- 92%of identities with sensitive permissions did not use them in 90 daysSonrai, enterprise cloud tenants
- 82 to 1machine identities to humans, and most standing privilege sits with themCyberArk 2025 Identity Security Landscape
The moment
The admin role was granted for one incident in April. It is October. Nobody has used it since, and nobody has taken it away.
For the team that grants privilege and has to take it back.
Every elevation has an end time
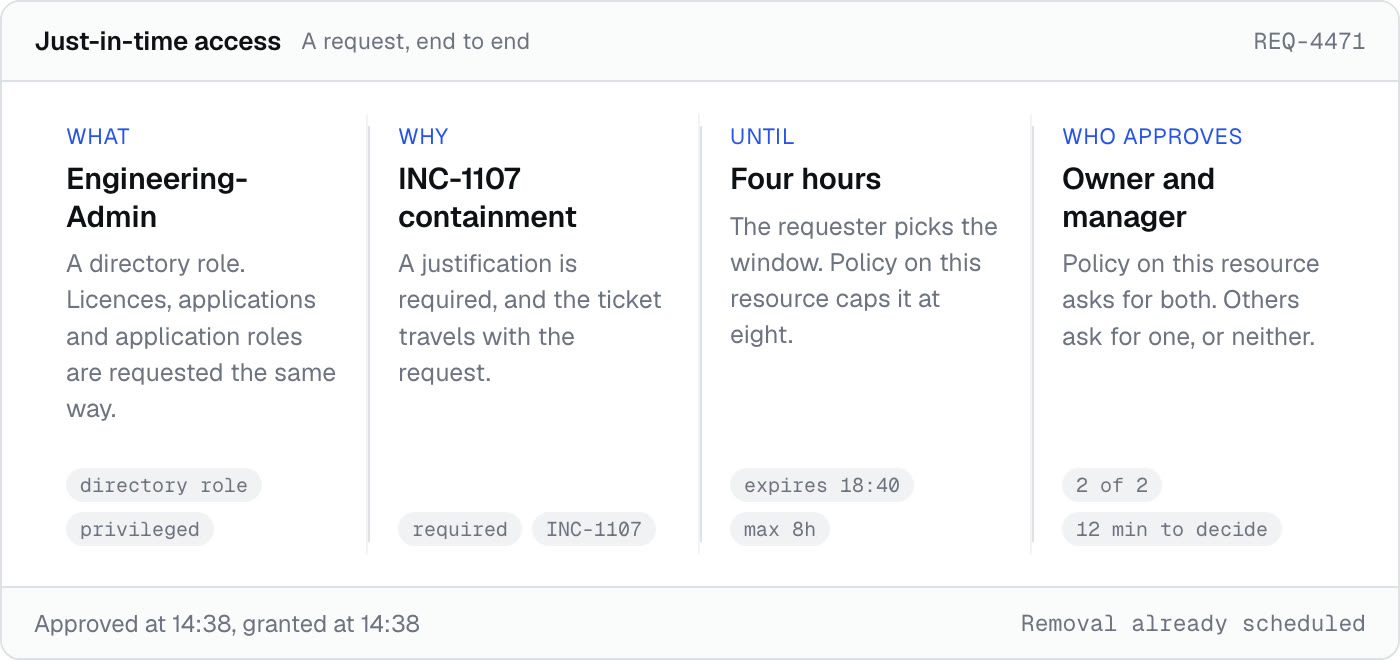
A license, an application, a directory role or an application role, all requested the same way, none of them granted open-ended.
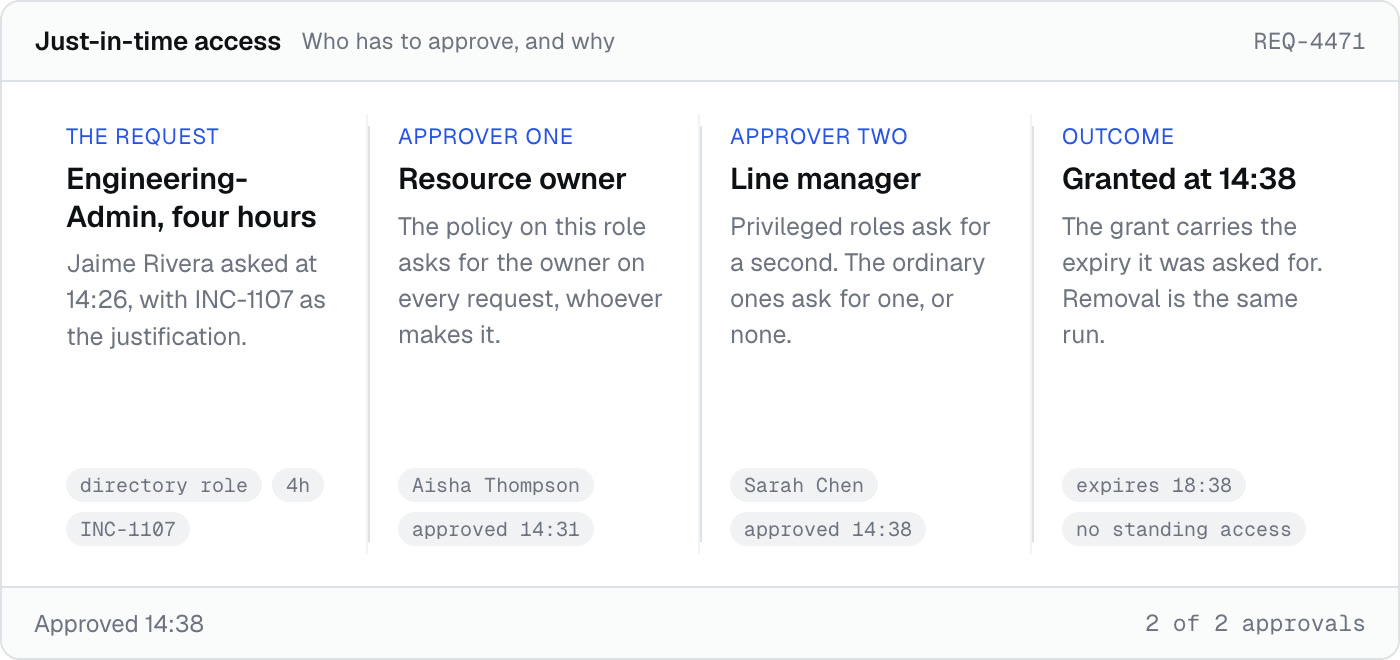
Policy on the resource decides who approves
The resource owner, the line manager, or both. The risky resources ask for two people and the ordinary ones do not get in the way.
Removal runs on the expiry
The schedule that granted it takes it back, whether or not anyone remembers.
What you get
Everything this covers.
Request
- A license, an application, a directory role or an application role
- A justification is required and the ticket travels with the request
- The requester picks the window, policy caps how long it can be
Approval
- Policy on the resource routes to the owner, the manager, or both
Grant and expiry
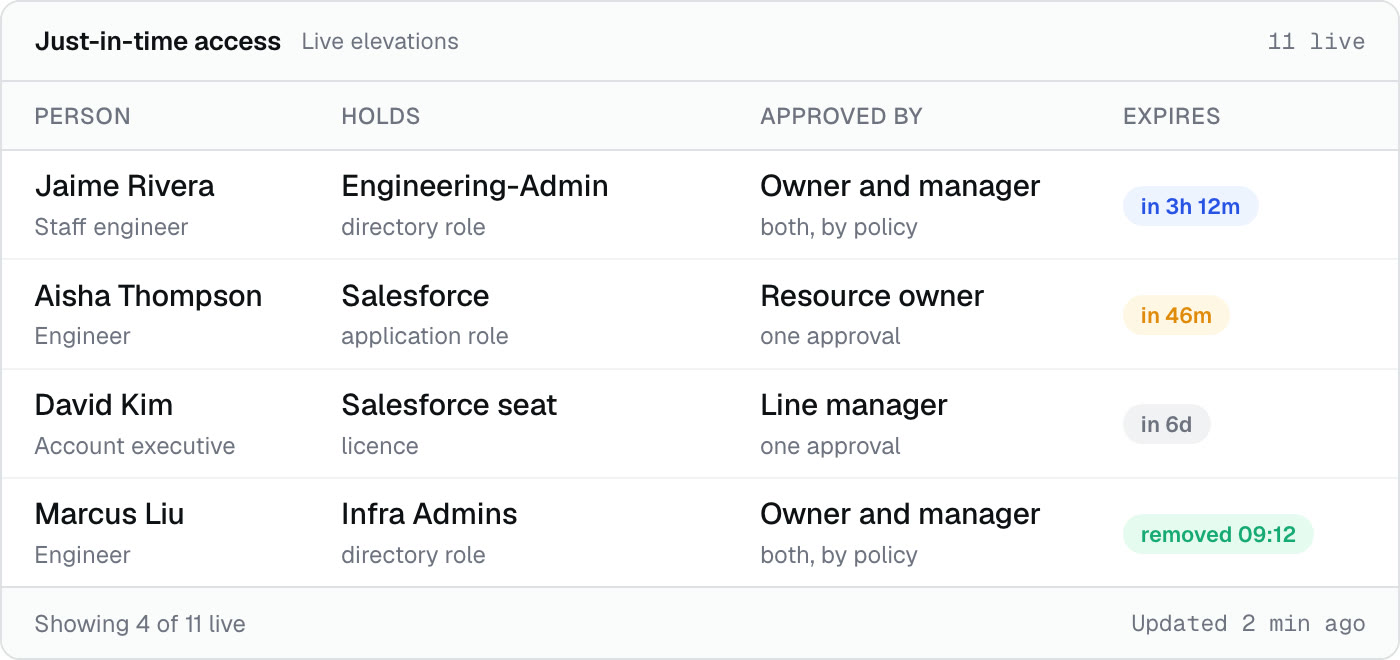
- Removal runs on the expiry time itself
- Every live elevation shows who approved it and what is left
- One record per request: asked, approved, granted, removed
Assurance
- What stays standing is small enough for a review to cover