Govern and Posture
Nobody owns this account
Every service account, key and token gets a name against it.

What the industry reports
- 82 to 1machine identities to human identities inside the average organizationCyberArk 2025 Identity Security Landscape
- 44%growth in non-human identities in a single yearEntro Labs, H1 2025
- 87%of the identities holding unused sensitive permissions are machinesSonrai, enterprise cloud tenants
The moment
The deploy account was created for a migration two years ago. The engineer who made it has left. It still holds Directory.ReadWrite.All.
For the platform team that inherited them.
Classification comes from behavior
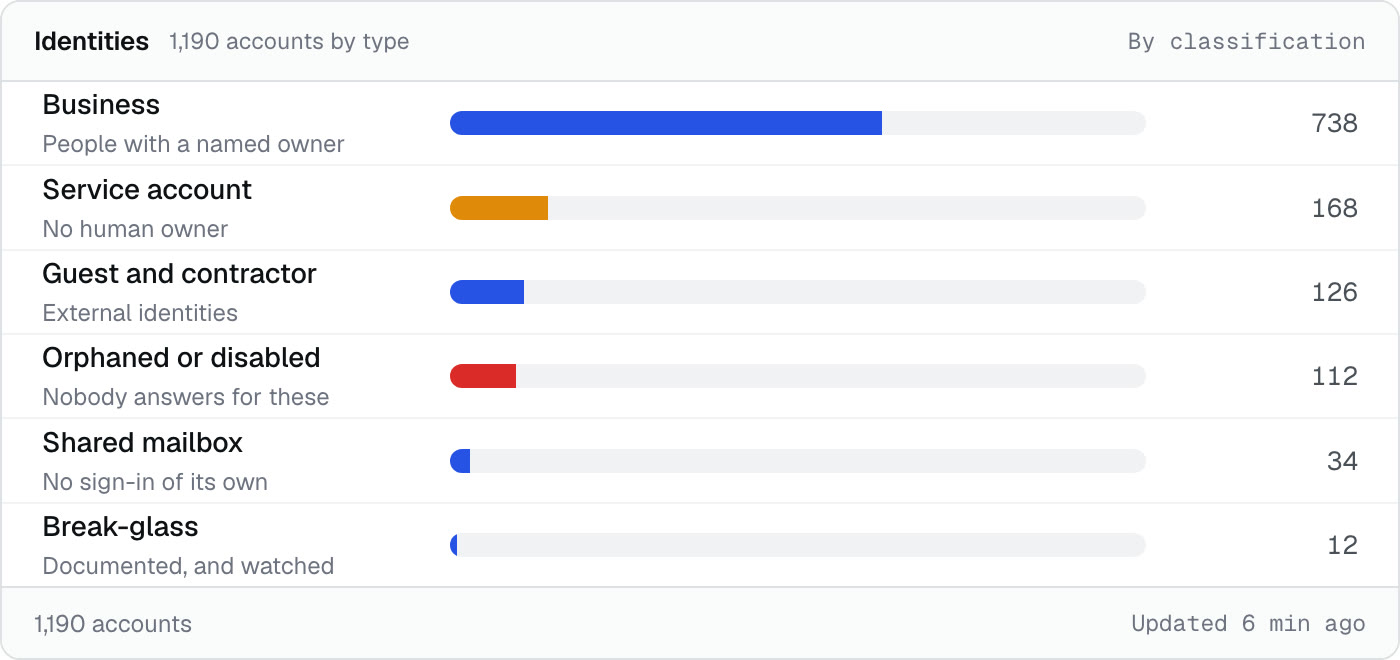
Service, break-glass, shared mailbox and resource accounts are told apart by how they are used, whatever they were named.
They sit in the same graph as the people
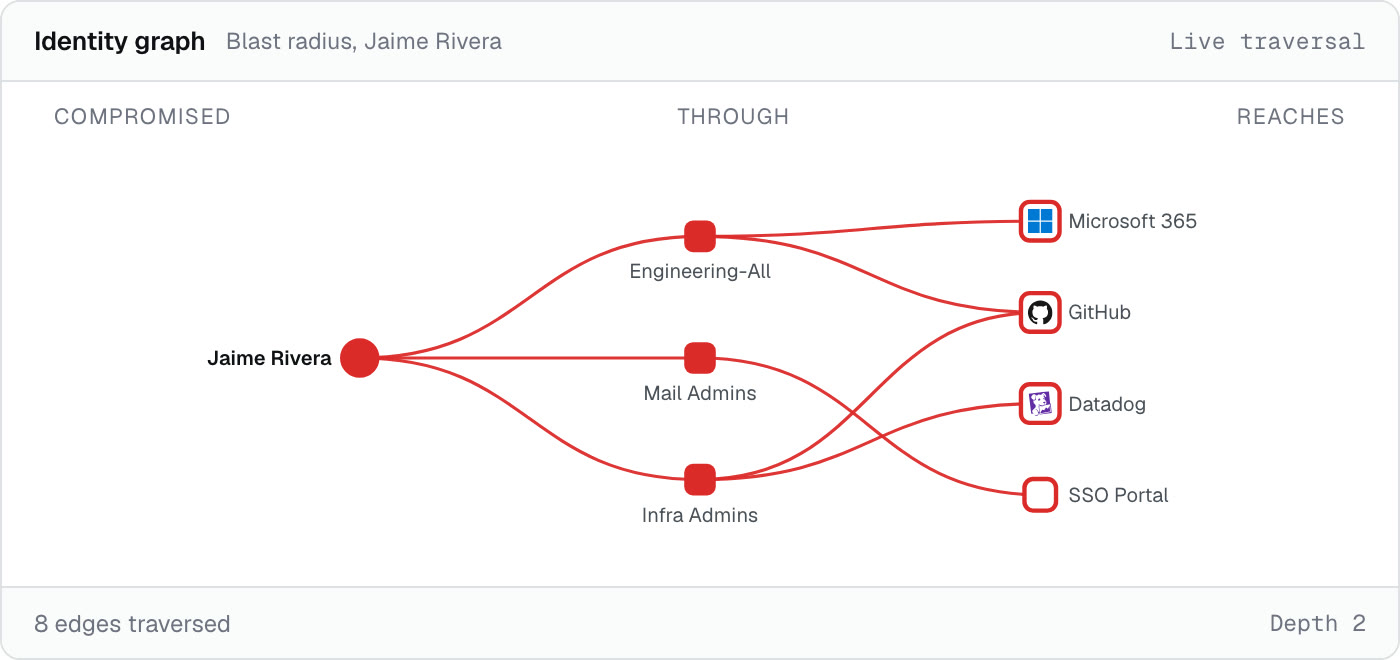
A dormant deploy account holding Global Administrator is comparable to a person holding it, because reach is measured the same way for both.
Dormant comes with a date
Last sign-in travels with the account. An account with no sign-in in four hundred days is a different conversation from one running every hour.
What you get
Everything this covers.
Discovery and inventory
- Every service account, key and token in the directory and the applications
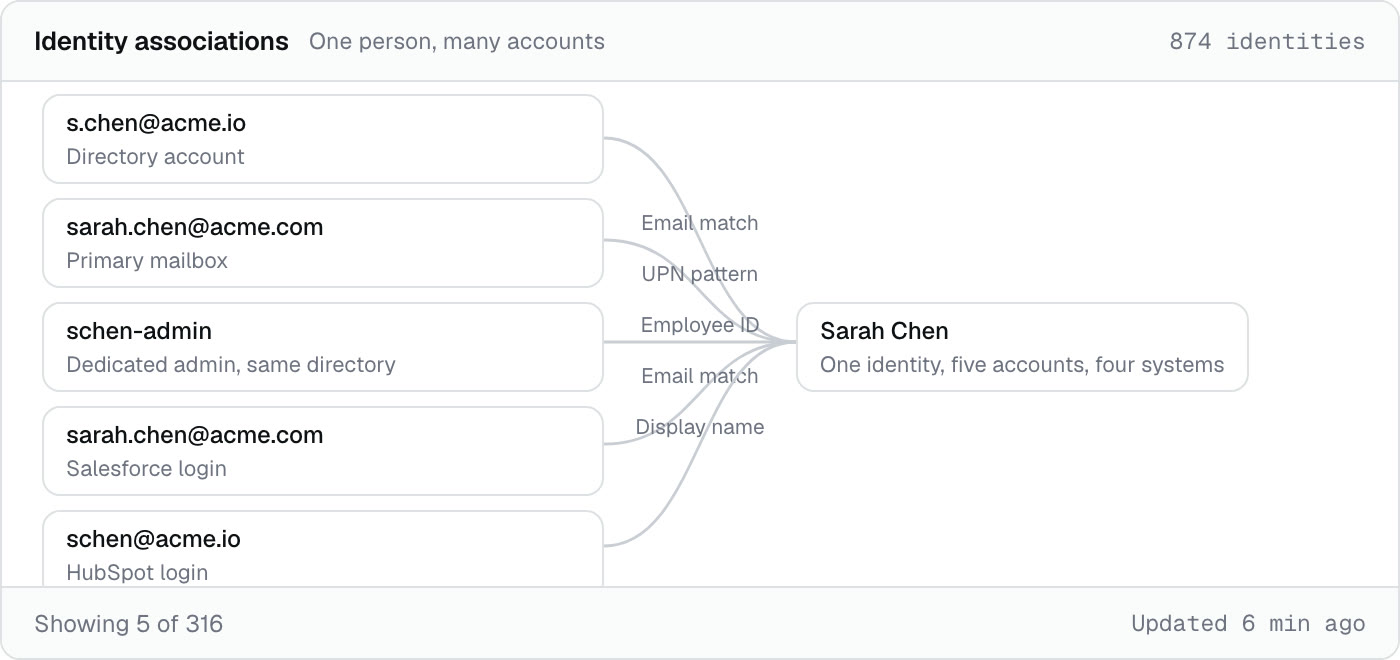
- Accounts matched automatically, and linked by hand where they are not
- Re-classified on every sync, one account at a time
Classification and ownership
- Service, break-glass, shared mailbox and resource accounts told apart
- Classification from how the account behaves
Entitlements and reach
- Non-human identities sit in the same graph as the people
- Blast radius comparable between a person and a service account
- A last sign-in date on every account, human or not