What the industry reports
- 55%of permissions were classified safe and compliant in 2025, down from 70% the year beforeSonrai, cloud permissions analysis 2025
- 28%of permissions are now ungoverned, up from 5%Sonrai, cloud permissions analysis 2025
- 92%of identities holding sensitive permissions did not use them in 90 daysSonrai, enterprise cloud tenants
The moment
The auditor wants proof that every privileged account was reviewed. The last campaign lives in a spreadsheet somebody exported in March.
For the GRC lead who owns the evidence.
Every decision carries its evidence
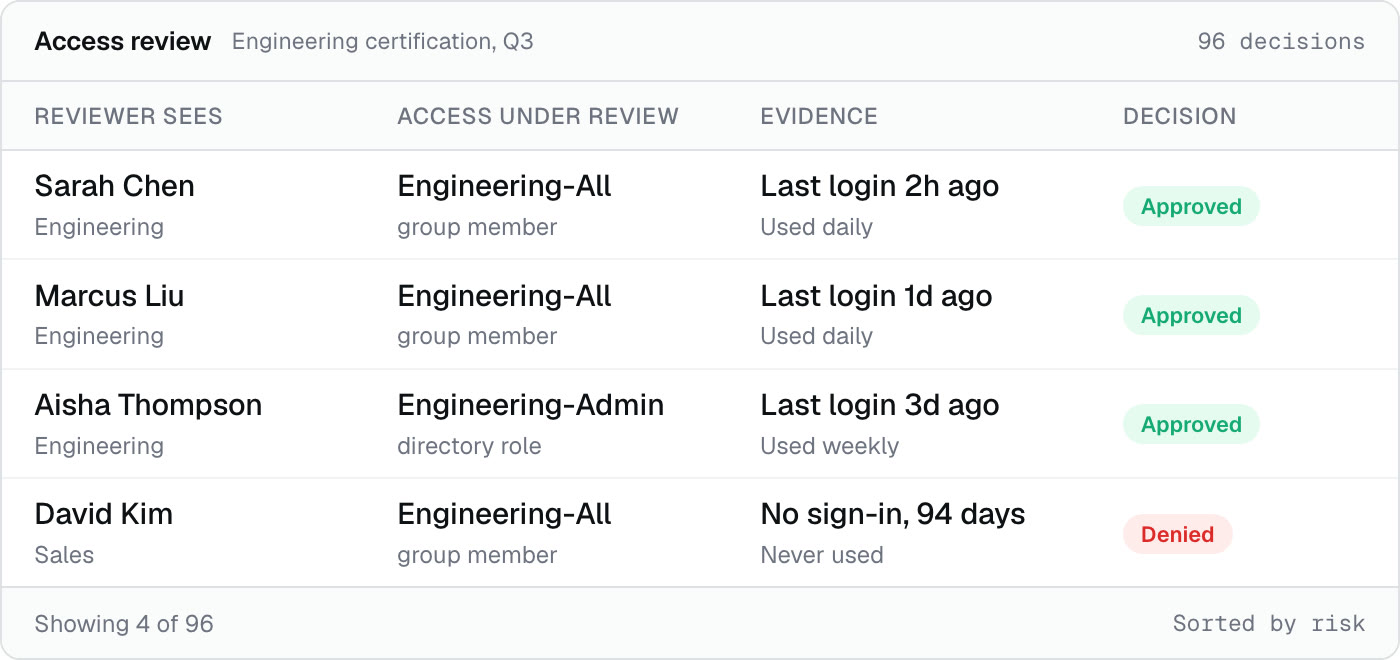
Last sign-in, how often the access is used, and a flag on anything unused for ninety days, on the row being decided. The reviewer is not guessing and neither are you.
A denial reaches the directory
Application access, group membership and directory roles come off per account once the review closes, and a failed revoke is reported per account.
The record is the audit trail
Every decision names who made it and when. Hand that over.
What you get
Everything this covers.
Identity lifecycle
- The directory change drives joiner, mover and leaver
- Birthright access by role and department when the account is created
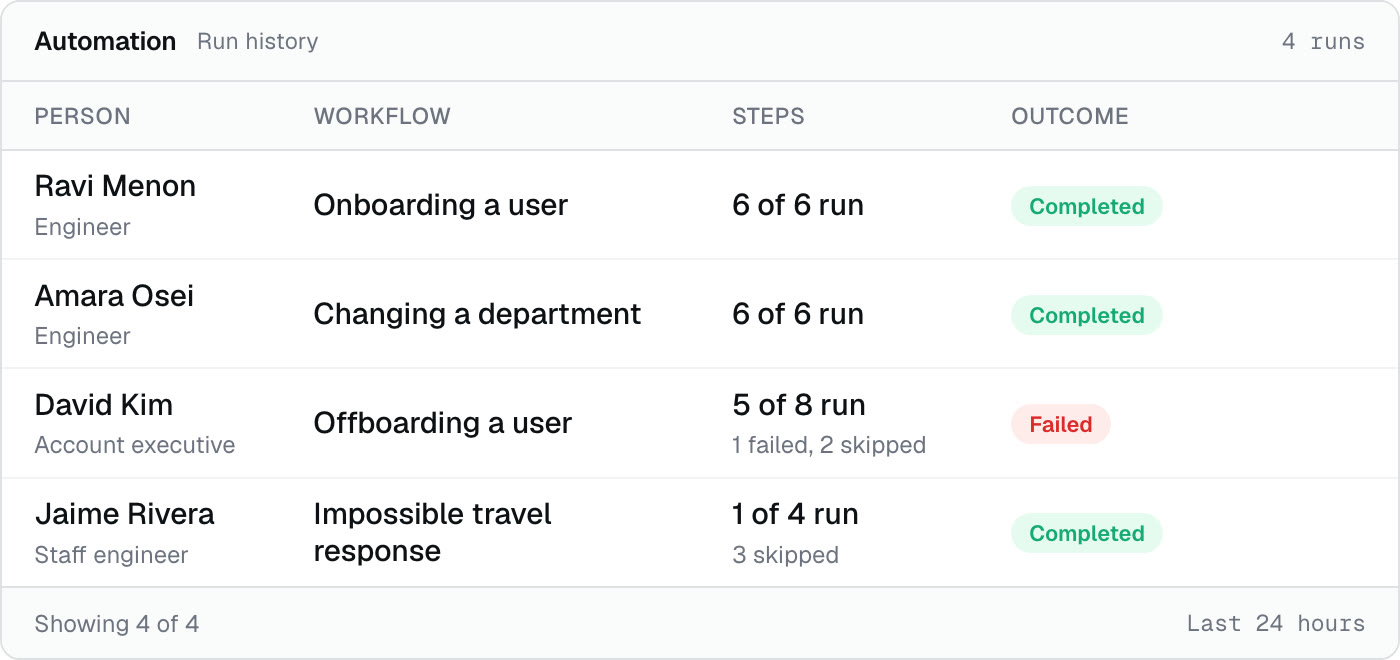
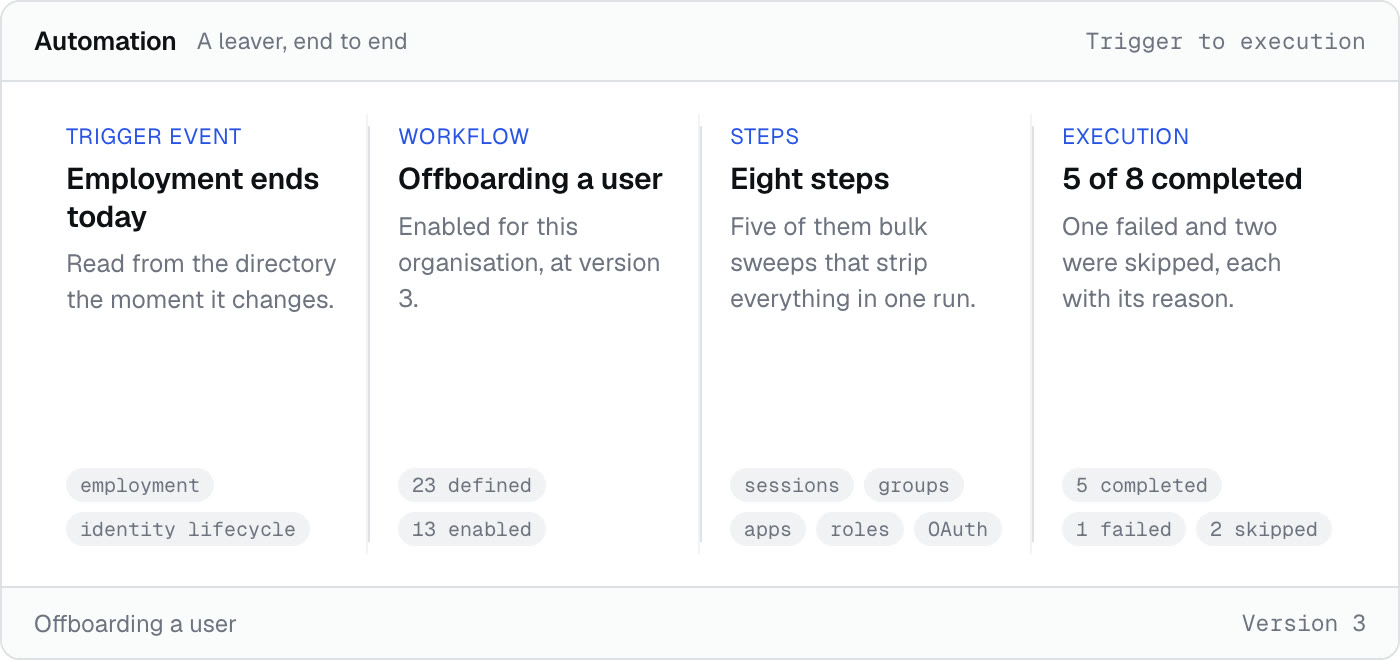
- Sessions, groups, app assignments, roles and OAuth grants stripped in one run
Access certification
- Campaigns over tags, groups, applications or directory roles
- Ordered reviewer stages with a fallback reviewer on each
- Last sign-in and usage on the row being decided
- Bulk-approve the obviously fine, spend the time on the rest
- Recurrence with an end date or an occurrence cap
Policy and role management
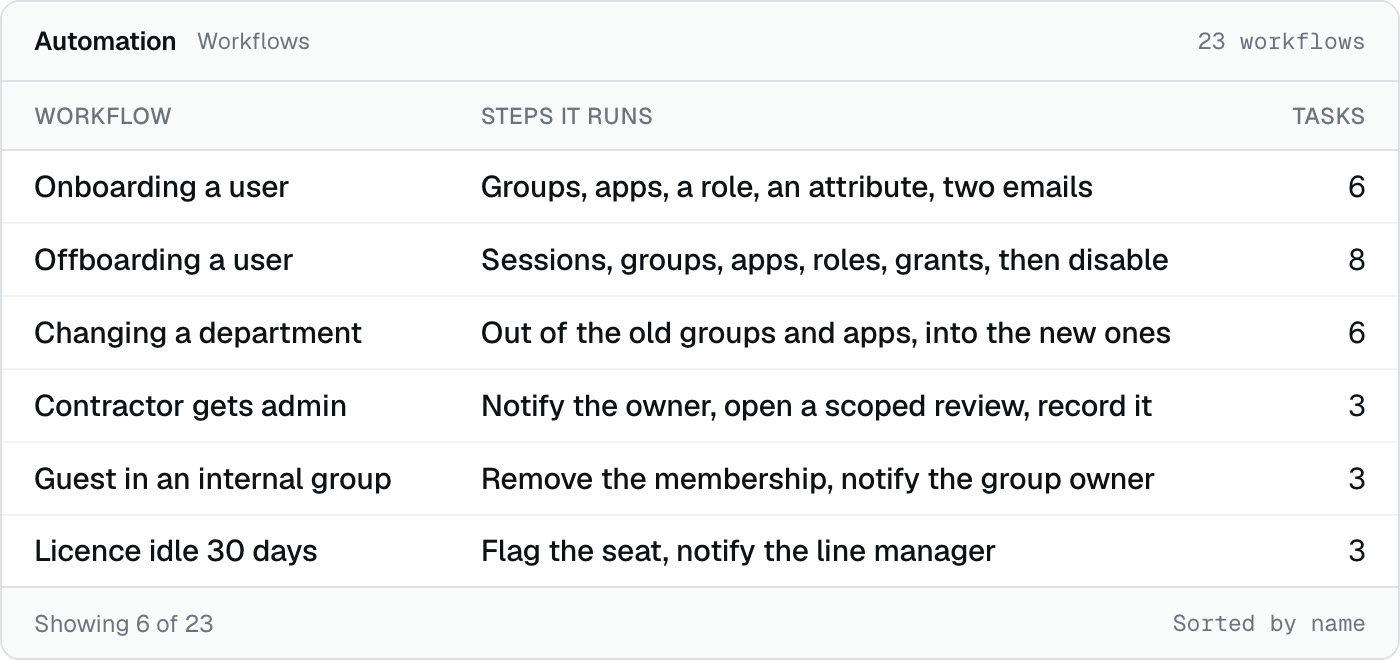
- A policy binds a trigger and a population to one reusable workflow
- Workflows versioned, with a snapshot of the version that ran
Audit evidence
- A denial revokes application access, group membership and directory roles
- A failed revoke reported per account
- Sign-off recorded against a named person, with the date
- Evidence exports as a CSV of every decision